抄作业 / 做成了什么 / Grok Bot
SuperGrok Heavy policy_denied evidence hub
标题与摘要为原文,未翻译。
- 做了什么
- Privacy-sanitized public evidence hub for an unresolved SuperGrok Heavy to Cursor Grok Bot linking failure that returns policy_denied on a paid feature path.
- 场景
- 安全与隐私
- 资料完整度
- 作者与原链接有
- 做了什么有
- 来源原文摘录有
- 截图 / 媒体有
- 步骤 / 章节有
- 提示词 / 配置原文来源未提供
- 结果 / 数字来源未提供
- 风险提示有
- 相关条目有
— 表示来源没有给出,本站不补写。
- 来源原文摘录
> September 11 support correction: Cursor now says different emails can link and attributes this case to a .ru domain restriction. On September 12, the customer clarified that the long-standing email and X-authenticated Grok identity must remain unchanged; changing the address is not an acceptable resolution. No supported remedy has been verified. Read the correction and September 12 follow-up. Earlier statements and downloadable packets are historical snapshots.
RongleCat/awesome-grok-bot (GitHub) · 打开原文 ↗ 摘自项目 README,照录原文,未翻译。
- 效果截图
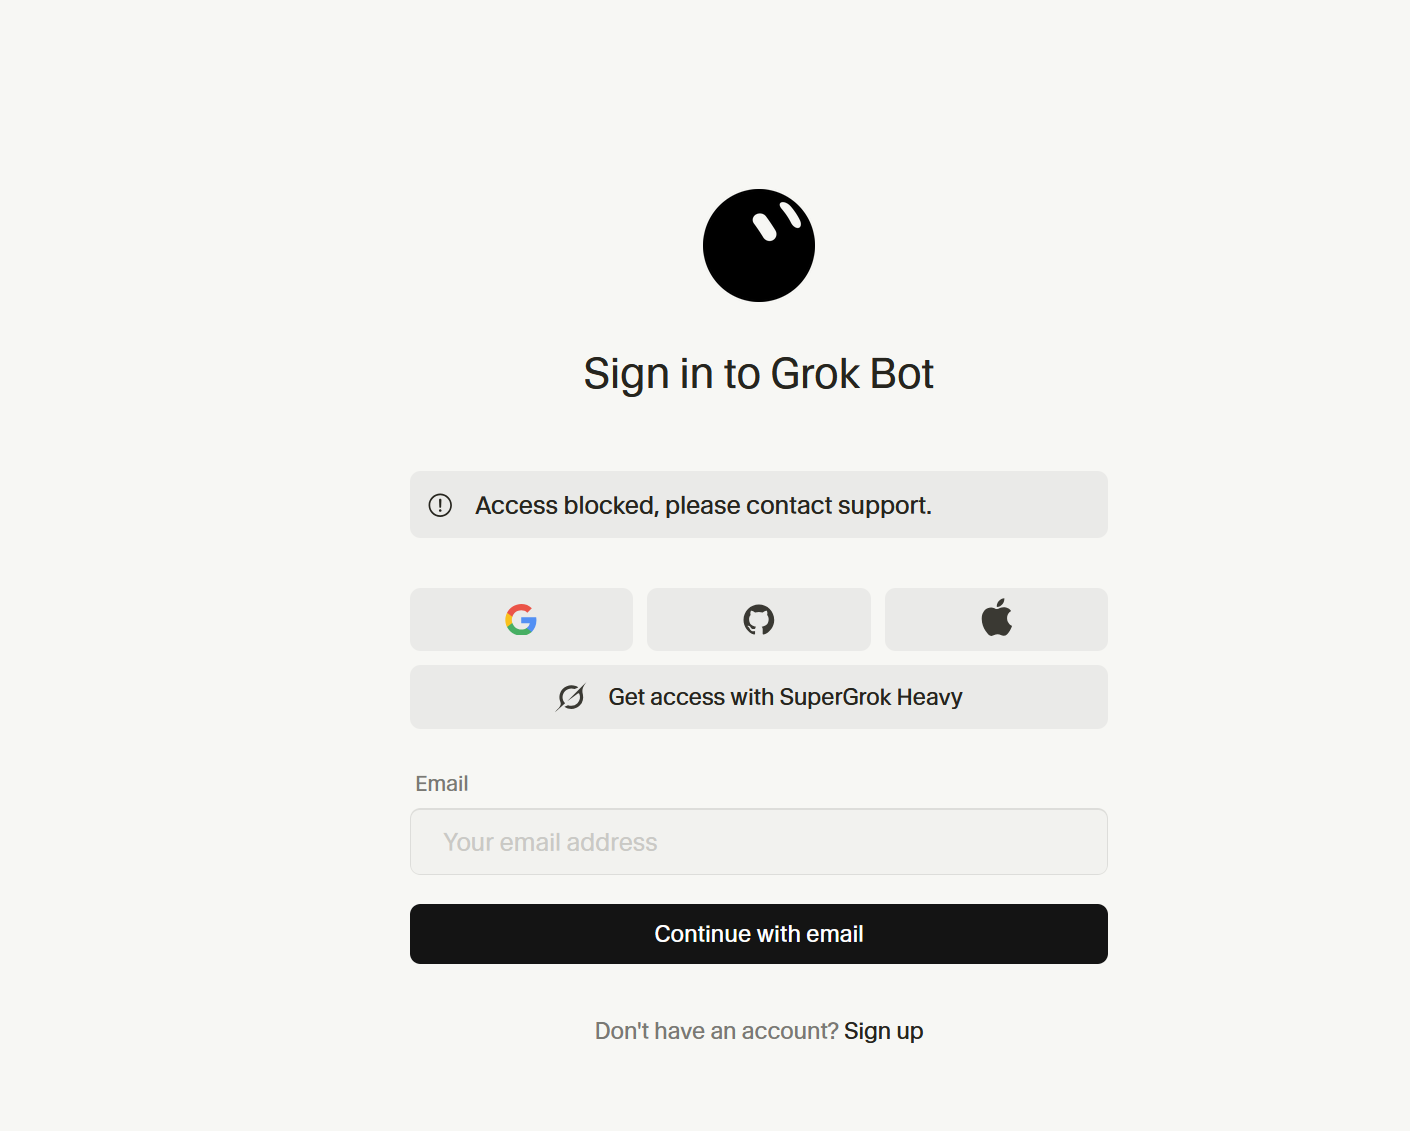
图片来自项目 README - 来源里的步骤 / 要点
- Open the public incident page
- Read the public incident brief
- Give the technical owner this action packet
- Inspect the system reconciliation matrix
- Audit the evidence chain and proof boundaries
- Inspect the public-source matrix
- Inspect neutral first-party archive preservation
- Audit the authentication path
照录来源原文,未翻译。
- 提示词
来源没有给出可直接复制的提示词原文。
- 怎么复制
- 打开仓库:github.com/COOLak/cursor-grok-bot-policy-denied ↗
- 读 README,把仓库链接发给你的 Bot,让它按 README 复现
- 先在小范围跑通,再加 routine
- 风险与限制
- 会读写你的邮箱:先只给只读和草稿权限,发信前人工审批
- 作者的结果不保证能复现,以原帖为准
- 用量预估
- 用金属计算器估一下